Sunday, October 21, 2012

Product review: Republic Wireless Defy XT 557

I admit: I'm a luddite. Although I worked as a mobile software developer for several years, I'm one of the last to acquire a smart phone. But now, I am the owner of a Motorola Defy XT, thanks to Republic Wireless. I guess that it's about time that I joined 2010 (my previous phone is a Verizon Samsung SCH-U620).


Frankly, I'm kind of pissed off that this has happened. Nobody does voice calls any more. Everyone seems to want to live a quiet, silent life of text messaging. When I ride mass transit, people look at each other when they make voice calls. I was very happy with my itty bitty Samsung device with physical buttons that fits conveniently in my pocket, but not happy with the prospect of paying $60 per month for a data package that I deemed useless. Republic Wireless' voice roaming onto 802.11 wireless networks was just hackerly enough for me to appreciate their innovative business model, and actually want to try out their service.


I can do everything that I can do on the smartphone better on my netbook computer. As I've attempted to let the smartphone take over my life, I've noticed that it takes me a lot longer to communicate with others. I suppose that the smartphone thing is pretty cool for people who don't regularly touch type, but the lack of a physical keyboard is a serious drawback.

However, the ubiquitous 3G data roaming onto Sprint's network within the greater Los Angeles area has been superb. I'm very impressed with how easy it is for me to do simple email communications and web browsing on the small platform. That stated, if I amortize the cost of the device out over one year, the device costs me $43 per month. At that price, it is extremely competitive with any existing Verizon wireless plan, and I have all of the features that I could possibly want. Plus, any dead zones that I regularly encounter on USC's campus are filled in with Republic Wireless' ability to roam onto wireless networks.

Overall, I'm really impressed with the product. My only quibble is that I cannot unlock / root the phone, because the SPC / MSL numbers don't seem to be readily accessible, although it's probably just a matter of time.

Monday, October 15, 2012

Setting up OpenVPN on FreeBSD

I've found a few tricks to help improve OpenVPN setup on FreeBSD. First off, there's a reasonably good PERL script that makes the process a bit easier. Install security/ssl-admin.

Next, set up your /usr/local/etc/openvpn/server.conf file:

proto udp
port 1194
dev tun
ca ca.crt
cert server.crt
key server.key
dh dh2048.pem
server 172.17.2.0 255.255.255.0

# Makes a local area network available to other clients
# This could be the IP block of your home network
push "route 192.168.1.0 255.255.255.0"
ifconfig-pool-persist ipp.txt
comp-lzo
client-to-client
duplicate-cn
user nobody
group nobody
keepalive 10 120
persist-key
persist-tun
status openvpn-status.log
verb 4
crl-verify /usr/local/etc/openvpn/crl.pem

Edit /usr/local/etc/ssl-admin/ssl-admin.conf.default and save as ssl-admin.conf in the same directory. Examples for the United States are shown below:

$ENV{'KEY_COUNTRY'} = "US";
$ENV{'KEY_PROVINCE'} = "CA";
$ENV{'KEY_CITY'} = "PASADENA";
$ENV{'KEY_ORG'} = "FOOBAR.NET";
$ENV{'KEY_EMAIL'} = 'CATS@FELINEHA.US';
Next, use the ssl-admin tool to create server certificates. Launch ssl-admin. You're presented with a "user-friendly" menu, but the menu requires knowledge about ssl certificate exchange. This knowledge isn't really necessary in order to set up a server. When the program initially executes, it will automatically ask you to create a certificate authority (CA) identity. Make sure you encrypt this certificate with a password. Next, choose options dh, and option S. Option S will prompt you for an "owner name." To make things less confusing, type "server" as the owner name.

Once these certificates have been generated, you'll want to copy them into your OpenVPN configuration directory:

cd /usr/local/etc/ssl-admin/active
sudo cp server.crt server.key ca.crt ../prog/crl.pem ../dh2048.pem /usr/local/etc/openvpn/

Edit /etc/rc.conf and add the lines:
# OpenVPN Server openvpn_enable="YES" openvpn_configfile="/usr/local/etc/openvpn/server.conf"

Configure your firewall to allow traffic into OpenVPN. If you use ipfilter, add the following lines to your /etc/ipf.rules file and then restart the ipfilter service:
# OpenVPN
pass in quick on XXXX proto udp from any to any port = 1194 keep frags
Now you should be able to start the OpenVPN server.
/usr/local/etc/rc.d/openvpn start

Server configuration is complete! Now you can create certificates for clients. I suggest creating  /usr/local/etc/openvpn/client.conf:
client
dev tun
proto udp
remote server.felineha.us
resolv-retry infinite
nobind
persist-key
persist-tun
remote-cert-tls server
ca ca.crt
cert client.crt
key client.key
verb 3

Make a symlink so this configuration is included in the client configuration archive:
ln -s /usr/local/etc/openvpn/client.conf /usr/local/etc/ssl-admin/packages/client.ovpn

Using the ssl-admin tool, choose option (4) to create certificates for a client. The script will prompt you for another owner name -- choose something that is descriptive of the remote host so that you can figure out what certificate is for what host.

When the script asks you "Can I move signing request (xxxx.csr) to the csr directory for archiving?", choose Yes. After the script creates the certificate for the remote host, choose option (z).

Although this blog post will get you started, some of the methods used are dated. Apparently Ubuntu 10.10 now allows import of  pkcs12 .p12 files. Essentially, these files replace the archive created by ssl-admin's option (z).

Monday, September 10, 2012

Concatenating PDF files using Windows Shell Add-ons

I was tasked with finding a good utility that would allow me to highlight a number of PDF files in the Windows Explorer, and then right-click to concatenate (combine) the files together to form one large PDF file.

PDFTk, the PDF toolkit, does this very well from the command line; however, the prospect of using a command-line tool is daunting to the average user.

I found a FANTASTIC tool called pdftk4all. It functions as a very easy-to-use front end to pdftk. Plus, it integrates a plethora of common features into a series of logical, easy-to-use contextual menus. As a programmer, one of the best features of this program is that its source code includes a very simple example of how to create cascading contextual menus for the Windows Explorer shell.

As best I can tell, there is truly no reason to purchase Adobe Acrobat.

Thank you to Maarten Veerman for PDFTK4ALL!

Sunday, September 9, 2012

A requiem for SharedCopy

The Internet did not shed a single tear this week at the demise of one of my favorite websites. I found Chew Choon Keat's SharedCopy to be incredibly useful, but it is now dead -- the website has disappeared, without a trace. I've scoured the search engines looking for information about the fate of SharedCopy.com, but nobody has said a peep. Along with the death of this website comes the disappearance of any information that I had saved using their excellent web annotation software.

This is yet another argument for using locally-developed, open-source tools to manage your own data, rather than using "the cloud." When will I learn?

Saturday, September 8, 2012

Getting spellchecking to work in LibreOffice / FreeBSD

I recently recompiled the LibreOffice port in FreeBSD and discovered that spell checking was not working. I installed textproc/en-hunspell and textproc/en-aspell and all was well.

PC-BSD 9 -> FreeBSD Notes

I've been using PC-BSD 9 for a while, and I got sick of having only PBI (push-button installer) software installed, opting for a more traditional BSD experience of dependency hell. Here are a few tips for the uninitiated (notes for noobs) -- to help you get away from PC-BSD PBI updates and into FreeBSD source-centric happiness.
  1. Use portmaster to upgrade packages. It's really the way to go. In order to get portmaster, you can use the command: portupgrade -PN portmaster
  2. The first time you upgrade your packages, browse /usr/ports/UPDATING. When you update your packages, this is the first place to look when something doesn't compile. After you finish with your update, NOTE THE DATE OF THE UPDATE somewhere. That way, the next time you upgrade packages, you don't have to look through the entire /usr/ports/UPDATING file.
  3. Accelerate your life. Tell FreeBSD to find and use the fastest mirror site:
    1. portmaster ports-mgmt/fastest_sites
    2. /usr/local/bin/fastest_sites > /usr/local/etc/ports_sites.conf
    3. echo '.include "/usr/local/etc/ports_sites.conf"' >> /etc/make.conf
  4. PERL updates are funky. When updating PERL, you'll need to update the many PERL packages that are already installed on your system. The p5-XML-SAX- packages are temperamental because p5-XML-SAX-Expat modifies a file that is contained in p5-XML-Parser. I haven't bothered to understand the problem well enough to write a definitive tutorial here. You'll also need to update all p5- ports, as well as print/foomatic-db-engine because it, too, contains a PERL package.

  5. Make your fonts pretty. Everyone uses LCDs these days, so go download some patches to better support your eyeballs. The patches at https://github.com/paranormal/freebsd_fonts_ubuntu allow FreeBSD to use subpixel antialiasing. The only port that I needed to patch in order to make both Firefox and LibreOffice look beautiful was the freetype2 package.
  6. Update your kernel for the latest fixes. If you decide to update your kernel (at this point, there are lots of bugfixes in 9-STABLE), try SVN: 
    1. svn checkout svn://svn.freebsd.org/base/stable/9 /usr/STABLE
    2. mv /usr/src /usr/RELEASE
    3. ln -s /usr/STABLE /usr/src
  7. Do all your configs at once. When using the Makefiles in /usr/ports/..., all you need to do is make config-recursive. portmaster apparently does this by default; I haven't yet figured out how to cause the tool to prompt with all of the configs (maybe using the -P option has something to do with this).

Friday, August 31, 2012

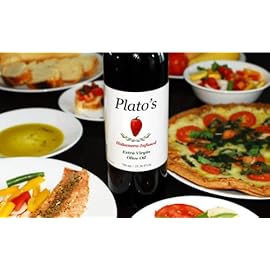
Product review: Plato's Habanero-Infused Olive Oil

Plato's Habanero Infused Extra Virgin Olive Oil (750 mL / 25.36 Oz, Mild)Plato's Habanero-Infused Spicy Olive Oil is a real treat. To date, my favourite pairing is to use the stuff on sandwiches; in general, it's just really really good on bread. Another great thing about the stuff is that you can adjust the 'spiciness' of a food just by adding more or less of the product.

As a supertaster, I really had never been a fan of olive oil because I thought that it tastes bitter and woody. I didn't know that olive oil can be sweet, fruity, and have a pleasing fragrance. My friend Mike has started a company that sells an infused extra-virgin olive oil that really surprised me. 

Give it a try!